Tokenization
Store once. Charge again and again.
Enable frictionless in-stay payments while protecting guest data. Tokenization keeps sensitive card details secure, never stored in your system and always PCI-DSS compliant.
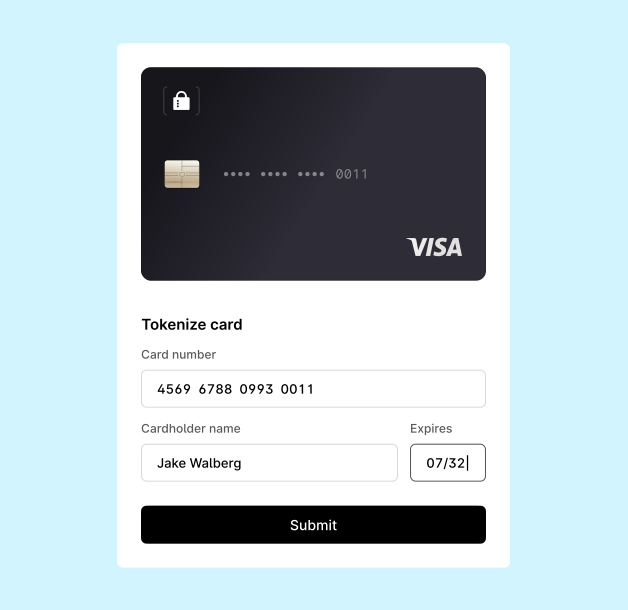
Simplify transactions. Guests enter card details once. Staff charges the token for incidentals, late fees, and upsells without re-swiping.
Reduce fraud and compliance risk. Card data never touches your system; tokens are encrypted and PCI-DSS compliant. Lower breach exposure, faster audits.
Capture more revenue. Frictionless charging means fewer missed in-stay charges (room service, spa, late checkout).
One fee, multiple properties.
Flat tokenization fee (not per-transaction) scales across all locations.
What is tokenization?
When a guest pays a property for the first time, online or in person, their card is securely tokenized and saved to their profile, making future payments fast, seamless, and friction-free.
Protect guests' details at all times
Replace sensitive card details with secure tokens, keeping guest payment information protected while enabling safe, seamless transactions across every touchpoint.

Make every guest payment seamless
Let guests pay effortlessly at POS, kiosks, during their stay and at check-out, without having to enter their card details again.

Built for compliance and cost control
PCI-DSS compliant and SOC 2 certified, tokenization protects sensitive card data, reduces security risks and simplifies compliance.